Ask me
anything

I’m trained by Dreeze on Dreeze so fire away and I’ll share more about our Application Revival platform.

The TL;DR on Dreeze

  • Backup & recovery
    for AWS and Azure

    Across accounts, regions, and Kubernetes clusters.

  • Autonomous app
    dependency mapping

    Dynamically built from what’s running,
    no tags or IaC required.

  • Data and configuration,
    backed up together

    Data copies plus all configs
    and keys each app needs.

  • Immutable,
    air-gapped vault

    Backups locked in a cyber vault you own.
    In compliance mode, not even admins can tamper.

  • SaaS-only, API-first,
    MCP-ready

    No installer and no in-guest agents.
    Open API and Dreeze MCP for your AI workflows.

  • Read-only in production,
    SOC 2 Type II

    Discovery through a read-only role
    and your data never leaves your accounts.

How Dreeze works

  • Scans accounts, regions, and EKS clusters every 24 hours or on demand
  • Reads 265+ connection types straight from resource configuration
  • Uses your tags, IaC, Helm, and namespaces as optional inputs
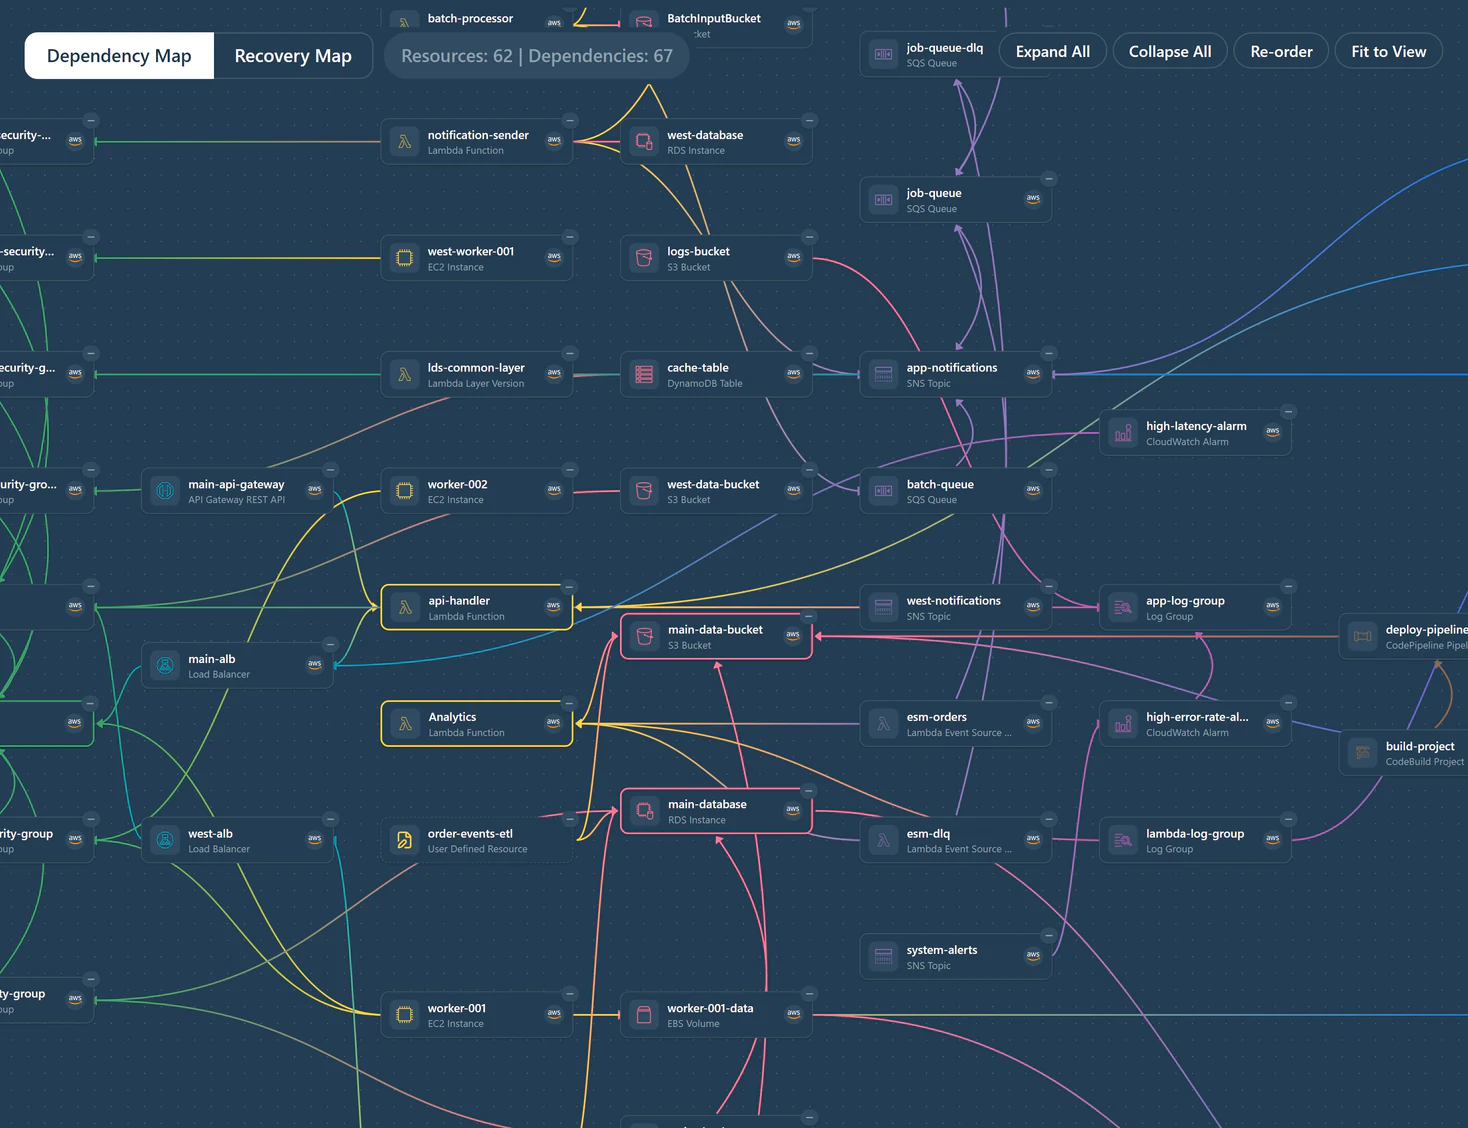
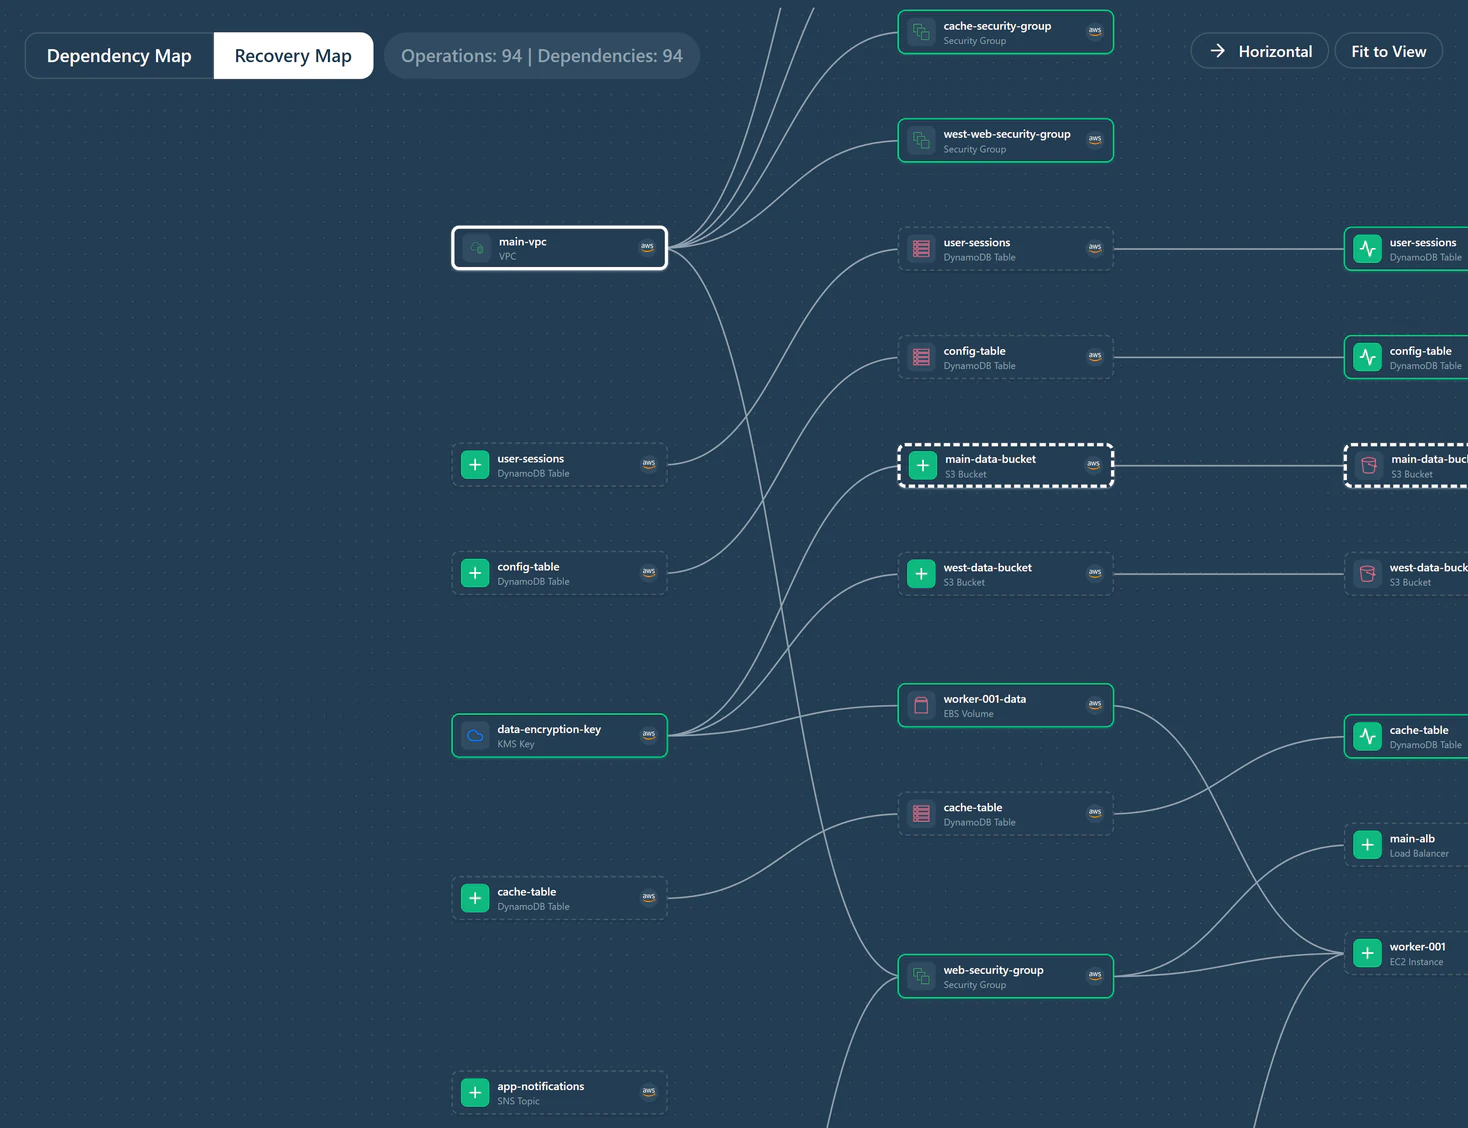
Dreeze dependency map showing the resources and dependencies of an application

  • Protect data: DBaaS, instance volumes, K8s PVs
  • Protect infra: subnets, security groups, load balancers, clusters
  • Protect config: IAM roles, keys, secrets
  • Auto-protect resources based on app, tags, namespace, or data sensitivity
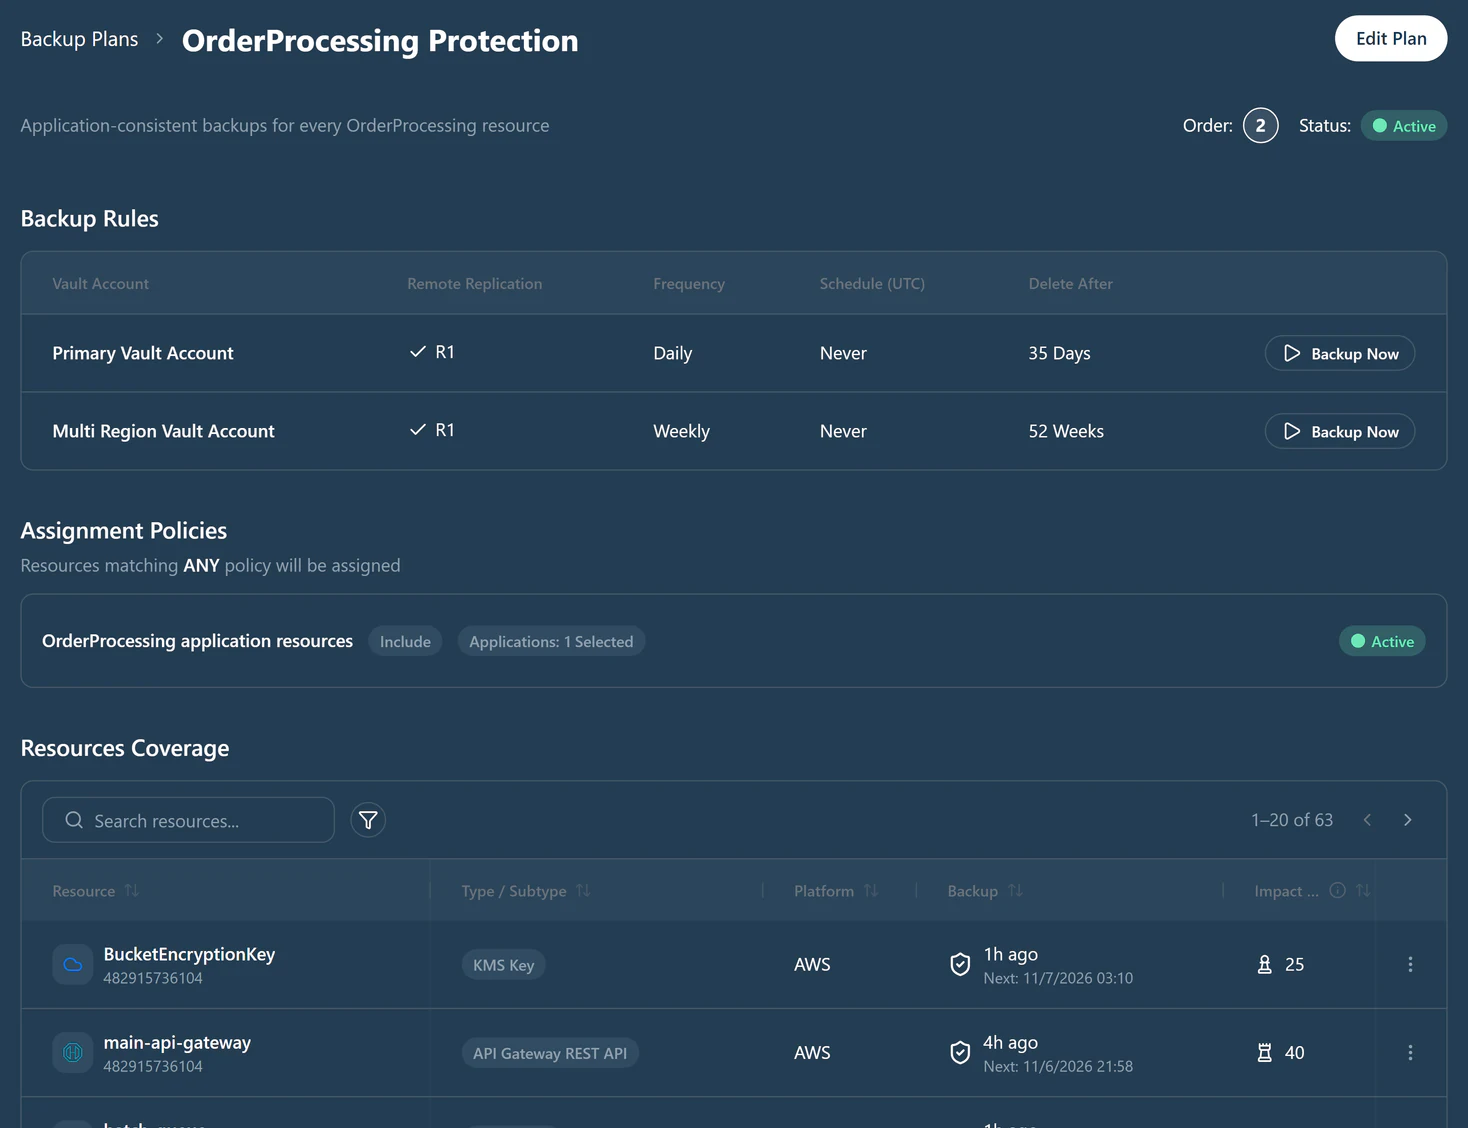
Dreeze backup plan with backup rules and resource coverage

  • Dedicated vault account in your tenant, locked with immutability
  • Encrypted with keys that never leave your account
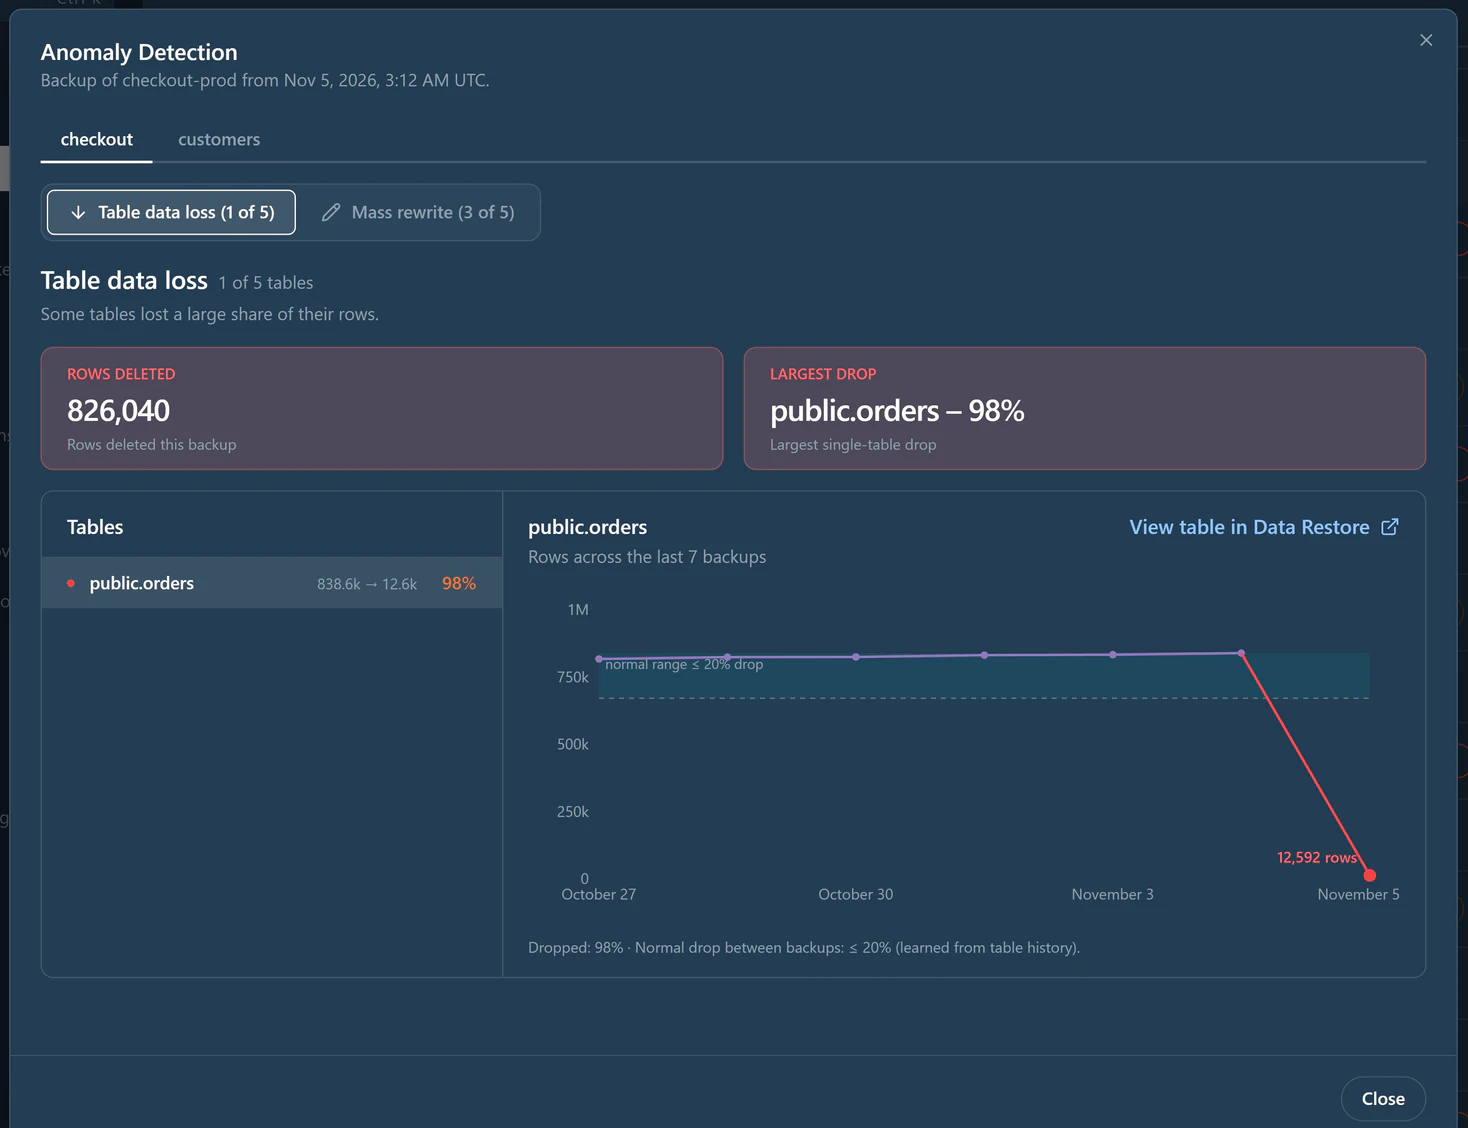
  • Anomaly detection flags bulk deletes or mass rewrites
Dreeze anomaly detection showing a table data loss in a backup

  • Revival plans are auto-generated from the dependency graph
  • Recover into any account or region, including clean room cyber recovery
  • Add custom steps for scripts or outside systems
Dreeze recovery map showing the operations to rebuild an application in order

  • Runs in an isolated account, then cleans up after itself
  • Non-disruptive tests, with config key review to keep test traffic away from production endpoints
  • Optional AI-assisted downscaling for recovery tests to reduce costs
  • Every test leaves a report of what ran, in what order, and how it went
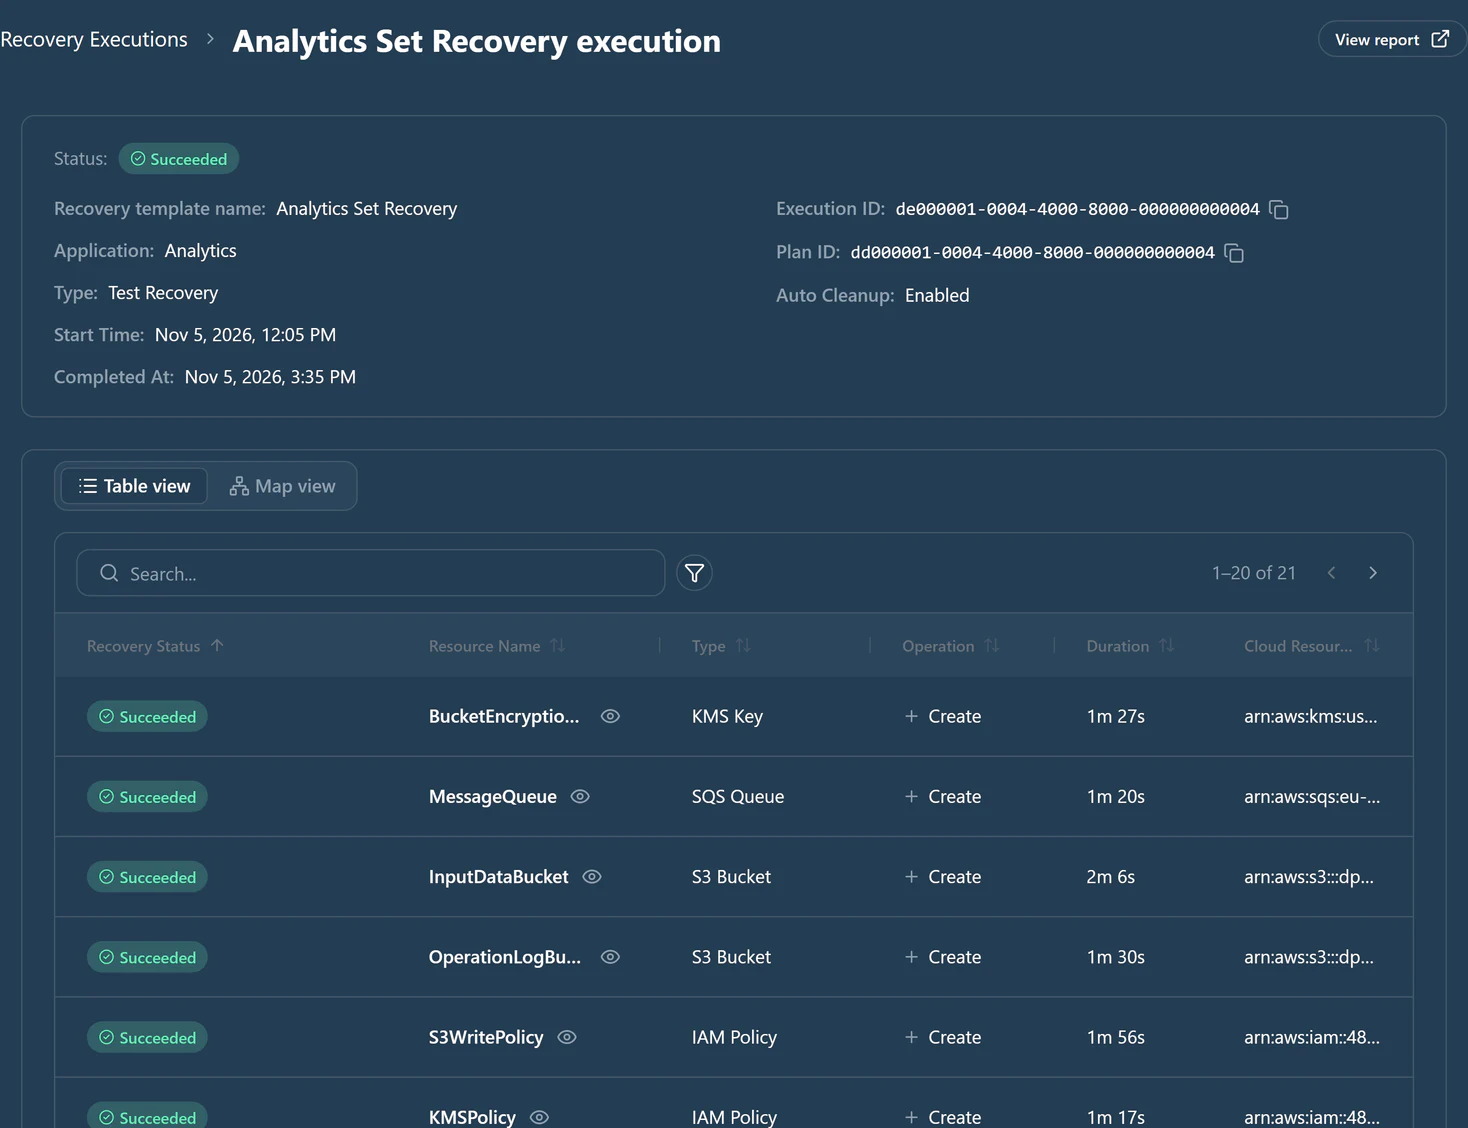
Dreeze test recovery execution with every resource recovered successfully

Ready to see Dreeze do its thing?

A read-only scan of one AWS account or Azure subscription maps your applications, their dependencies, and that one sneaky shared resource you had no idea was so critical.

Application Revival Explained

Explore the world of Application Revival with Dreeze.

FAQs

What is Application Revival?

It’s backup and recovery that brings back the whole cloud app, not just its data or individual resources. Dreeze backs up the infra, config, identity, keys, and secrets along with the data, rebuilds it all in the right order, and validates the rebuild before you need it during an incident.

What counts as an application?

An application is everything a workload needs to run, not just its data: compute, storage, networking, identity, messaging, keys and the connections between them. Dreeze discovers every resource in your live environment and groups them into applications using AI and code together, with membership always coming from the dependency graph.

Your tags, infrastructure as code and GitHub repos help if you have them, but Dreeze doesn’t need any of them. And you can adjust anything it finds.

What does Dreeze back up?

The data and everything around it, captured together at the same recovery point: databases, volumes and objects, plus the infrastructure, config, identity, keys and secrets the app depends on. The Revival Plans themselves are backed up too.

It all goes into an immutable vault in an account you own, and can be copied to a second region if you want.

Does my data leave my cloud accounts?

No. Discovery uses a read-only role and your data never leaves your accounts. Backups go to a dedicated vault account in your own estate, encrypted with keys that never leave your account.
Even a clean room recovery happens in your tenant, not Dreeze’s, so you stay in the driver’s seat.

How does Dreeze protect backups from ransomware?

Every app’s data and config land in a logically air-gapped vault account you own, locked the moment they’re written and encrypted with your own keys. In compliance mode, not even a compromised admin can delete them early.

Anomaly checks compare every backup to that resource’s history and flag bulk deletes, missing tables, slow drains and mass rewrites, so you can pick a recovery point from before the damage. Dreeze then rebuilds the whole app in an isolated clean room, where you can scan it with the security tools you already trust before anything reconnects.

Do I need clean tags or IaC?

No. Dreeze maps from your live environment, so you recover what’s actually running, not what someone meant to deploy. Your tags and IaC are optional inputs: if you use them, great, but Dreeze doesn’t depend on them, which matters most on the day your IaC no longer matches what’s running.

How often does Dreeze back up?

You decide. Set the retention policy per application to control exactly what gets backed up and how often, and Dreeze shows a cost estimate alongside it so you can compare it with what you pay today.

Dreeze rescans your accounts, regions and EKS clusters every 24 hours or on demand, and backup plans assign themselves by rule, so new or modified resources that match are covered automatically.

Will a recovery test affect production?

No. Dreeze runs the whole plan in an isolated environment without touching production, cleans up afterward, and leaves a report of what ran, in what order, how long it took and how it turned out. You can run tests on demand or on a schedule.

Production only gets touched if you say so.

Where does AI come in?

Dreeze AI takes on the heavy lifting, from autonomous dependency mapping to AI-assisted recovery tests, so you can scale your team without adding headcount. The Dreeze agent proposes app groupings and explains them, you can edit anything it proposes, and membership always comes from the dependency graph.

Dreeze always pairs AI with deterministic code, so it doesn’t hallucinate apps or act without your oversight. Prefer headless? Dreeze MCP lets your own agents check status, dig into a failed backup or kick off a test, and admins choose whether assistants get no access, read-only or read-write.

Who’s behind Dreeze?

Dreeze was founded by Ziv Kedem, co-founder and CEO, with his brother Oded Kedem and Avi Raichel. Ziv and Oded first worked together at Kashya, which built a continuous data protection and replication product and was purchased by EMC in 2006, where it became RecoverPoint. In 2009 they founded Zerto, developing disaster recovery technology for virtualized servers, and were joined there by Avi Raichel, previously VP Information Systems at Amdocs. Zerto was acquired by HPE in 2021.

Dreeze is their third startup, this time focused on backup and recovery for the cloud era.

Still have questions?

Ask the chat at the top of the page or get in touch with us.